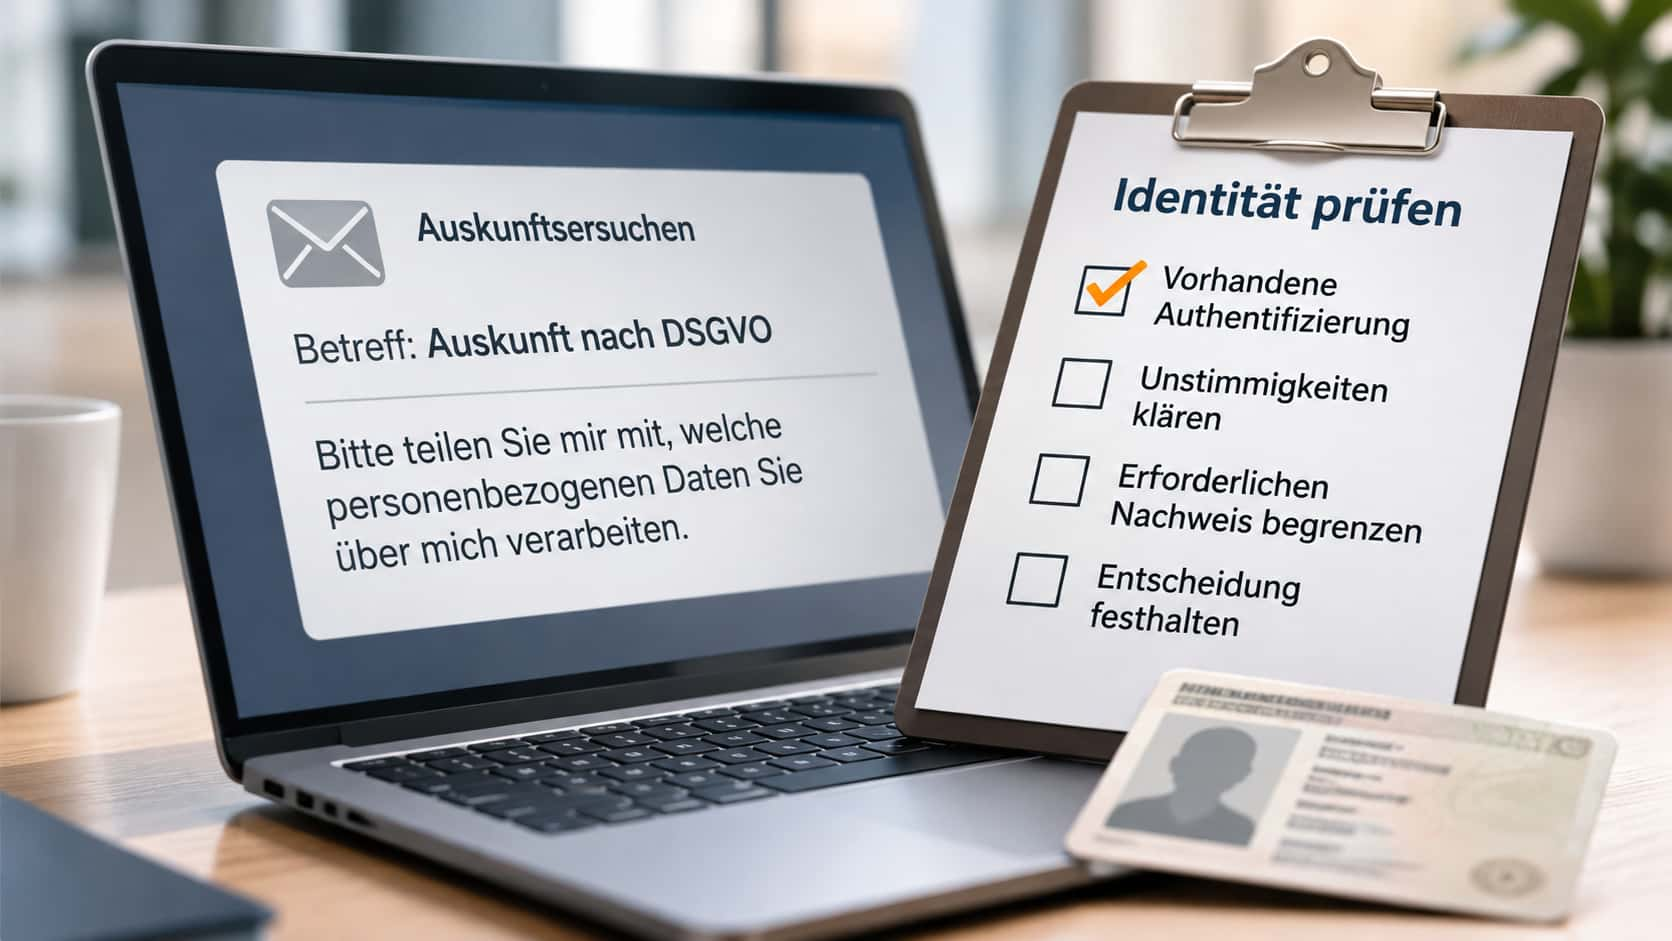
Providing information via email does not automatically require proof of identity. The key factors are specific doubts, existing authentication, and proportionate evidence.
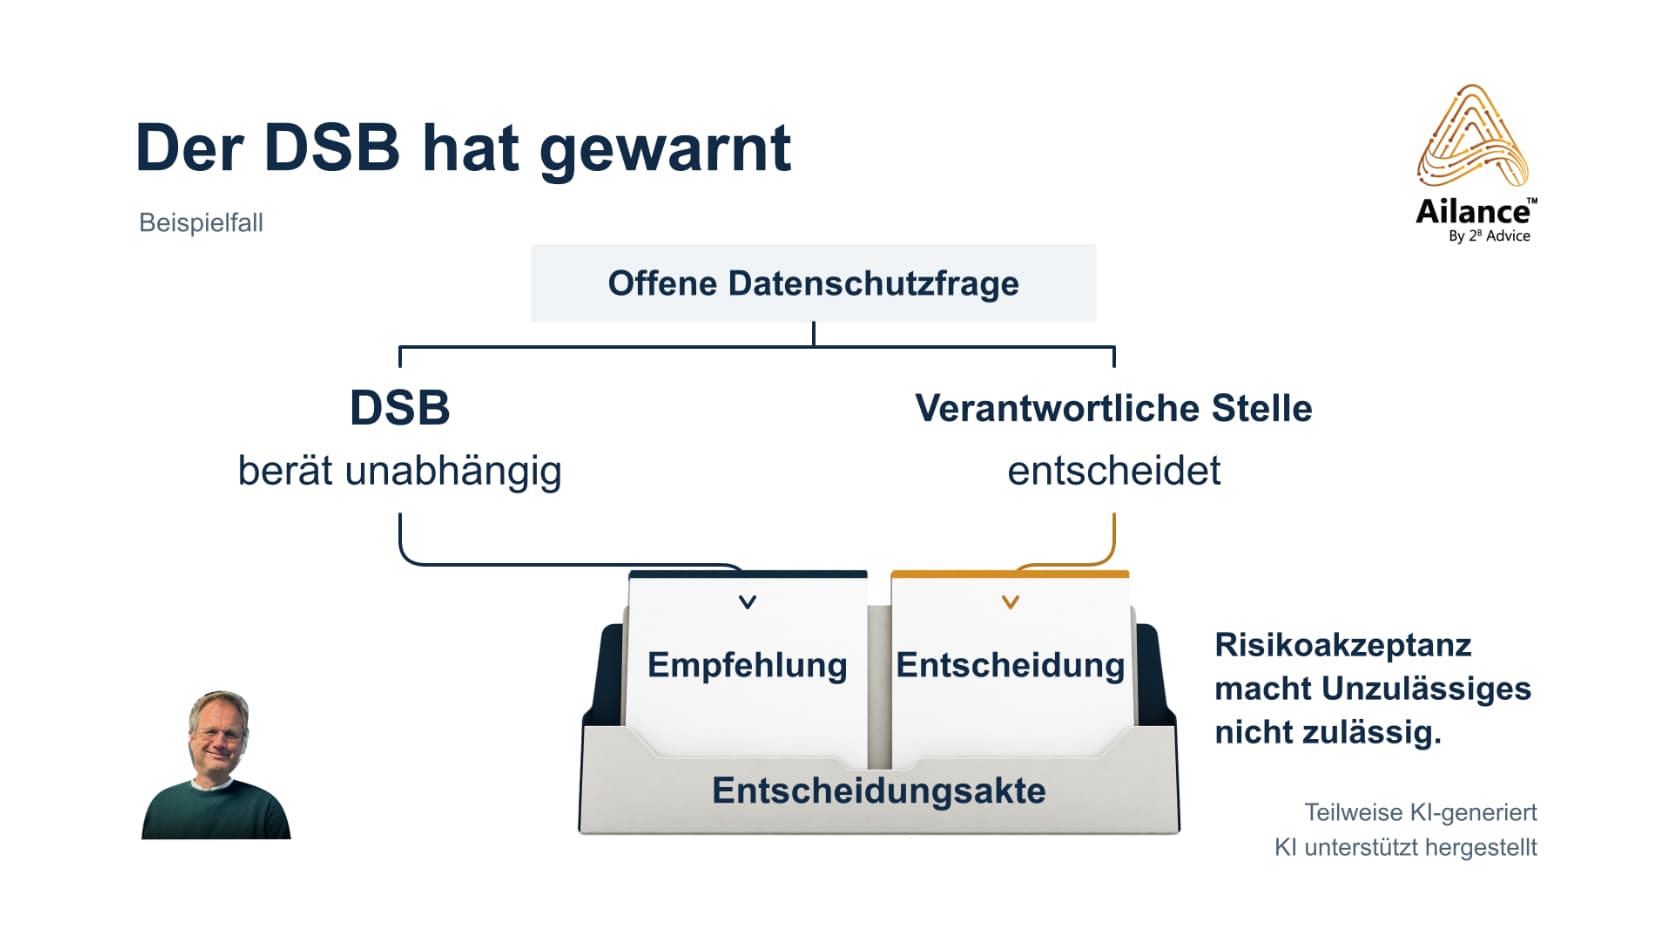
If the DSB issues a warning before a project begins, there must be clear lines of responsibility, legal boundaries, and a decision that is documented in a transparent manner.
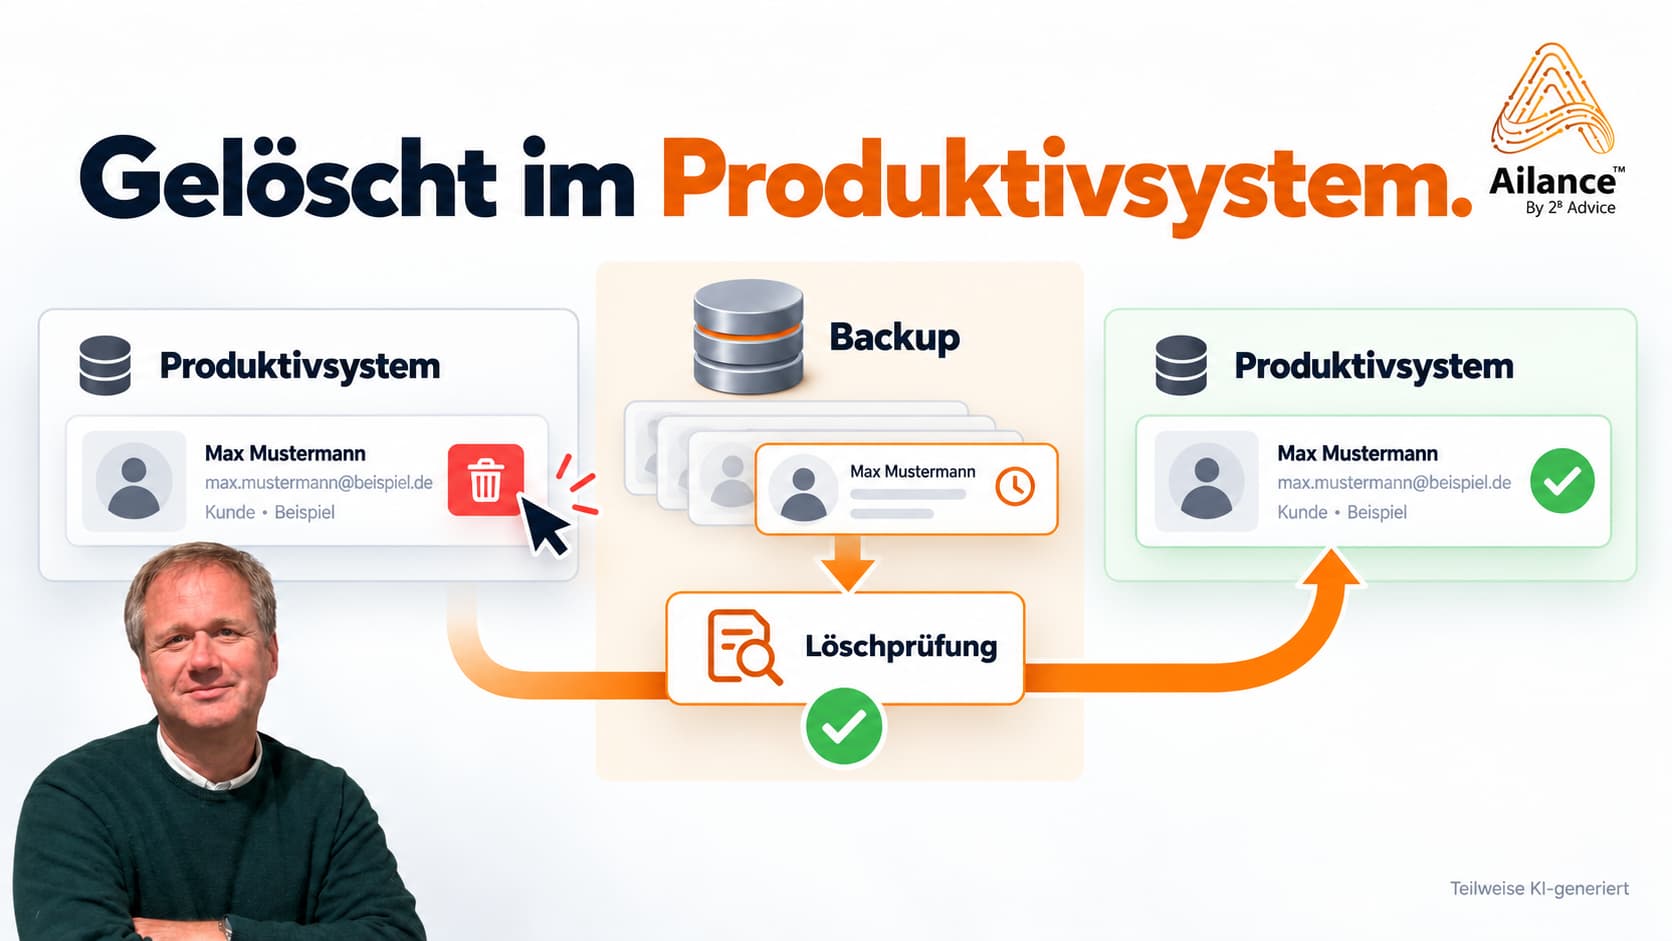
What happens to personal data if it has been deleted from the production system but is still present in older backups? This article explains how companies make decisions regarding the deletion of
Version control and audit trails in data protection software ensure that changes, approvals, and decisions remain traceable at all times—promoting greater accountability, auditability, and management confidence.
Sub-processes can structure Group RoPAs when comparable processes are carried out in multiple companies, countries, or locations with local variations. This article shows how master processing, variants, approvals,
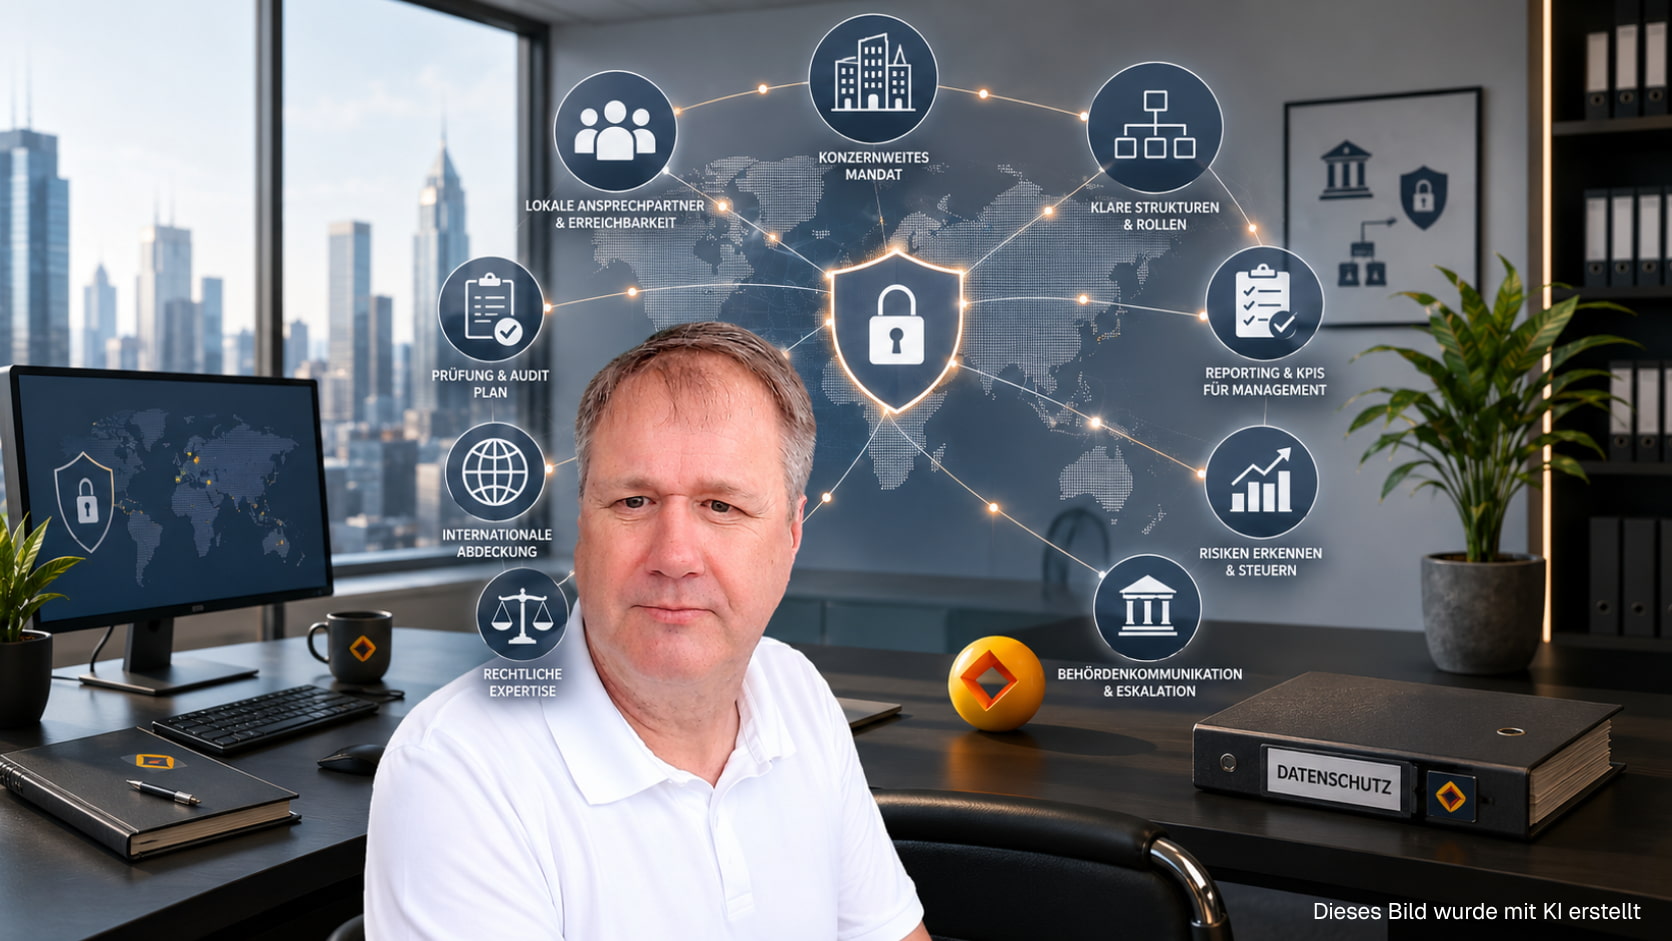
A corporate data protection officer requires more than just a formal appointment. What is crucial is a robust operational model with clear responsibilities, resources, reporting structures, audits, and escalation procedures.
Privacy-IRM software should not be evaluated solely based on feature lists. What matters most is whether roles, workflows, evidence, permissions, and operational risks can actually be managed within the ongoing governance process.
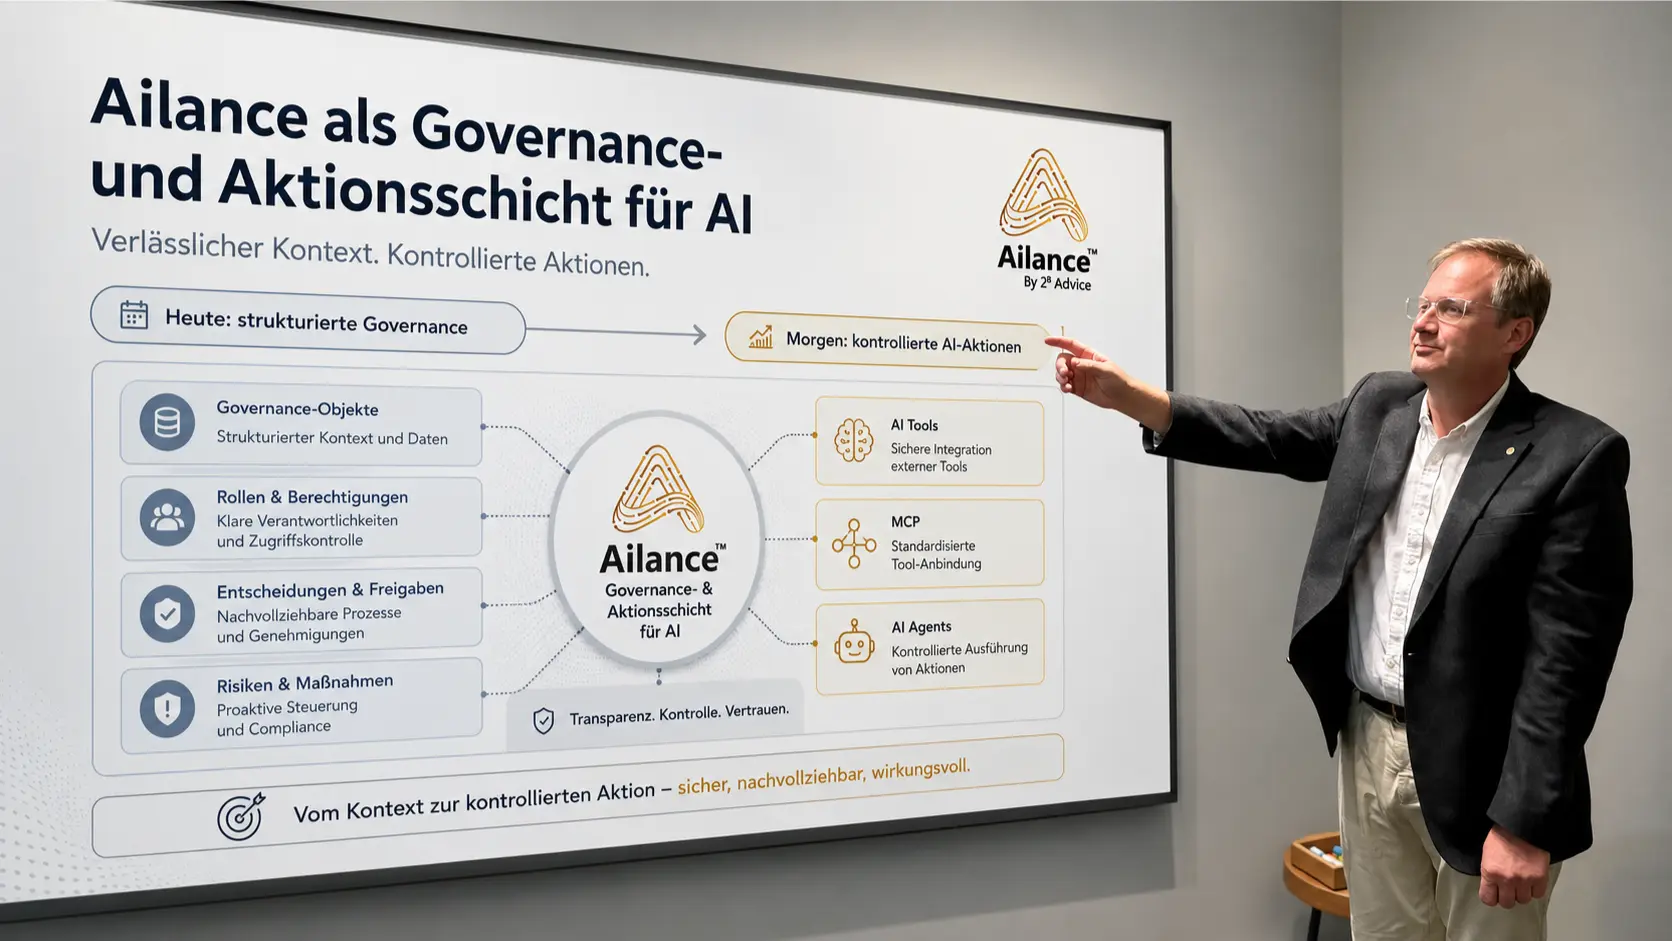
AI requires clear governance processes: use cases, risks, roles, approvals, and documentation must be brought together in a structured manner so that AI can be used safely and transparently within the company.